
Latest News
By now you are well-familiar with the protections that Cornell has to keep your NetID from getting hacked. Long passphrases and two-step login (via Duo) are two major shields. Safe Links and passkeys for staff and faculty are another pair in this defensive wall.
With these avenues of attack largely blocked, hackers have turned to social engineering to gain access to your account. But what exactly is “social engineering?”
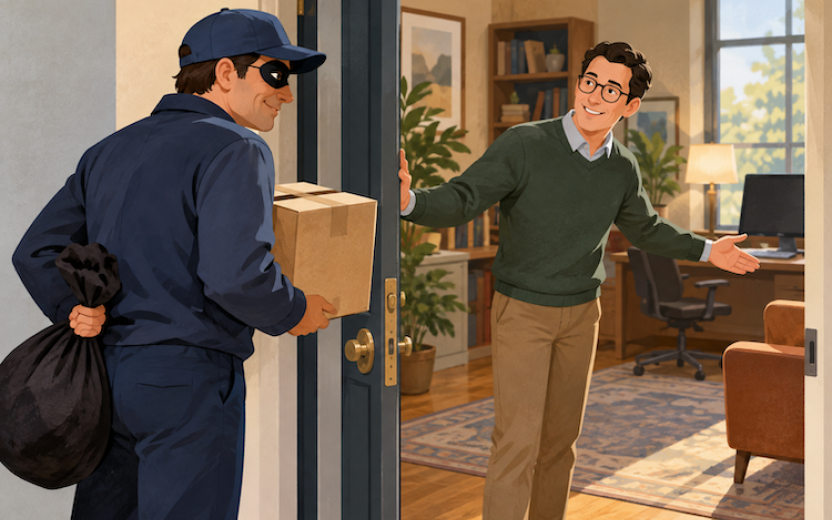
Social engineering attacks exploit human behavior instead of computer loopholes: the target is you not your computer. Think of it this way: A burglar can pick a lock, or they can put on a delivery uniform and ask to be let in. Social engineering is the uniform. The door's lock never needed to be broken because someone opened it willingly.
Key components of social engineering
Social engineering attacks often follow the same four steps. Knowing them makes it easier to spot one in progress.
1. They learn about you
Attackers look for details they can use to sound convincing, such as your name, job title, or who your manager’s name. They find this on social media, company websites, or in information leaked from past data breaches.
2. They pretend to be someone you trust
The attacker poses as a coworker, boss, IT support, a bank, or a well-known company. They may copy logos, mimic an email signature, or use an address that looks almost right.
3. They create pressure
This is the heart of social engineering. The message is designed to make you feel something so you act before you think. Common tactics include:
- Urgency: "Your account will be locked in 30 minutes."
- Authority: "This request comes directly from the Director."
- Fear: "We've detected suspicious activity on your account."
- Reward: "You've been selected for a free gift card."
4. They ask you to act
The final step is a specific request, such as clicking a link, opening an attachment, entering your password, approving a login prompt, or buying gift cards. Once you comply, the attacker can steal your information, install harmful software, or use your account to target others.
Watch out for this social engineering formula
Trust + Emotion + Action = Compromise
An email from an apparent source of authority, that plays on your emotions, and asks you to do something could lead to a stolen NetID.
Instead, follow this formula
Verify + Breathe + Wait = NetID safety
Check the email against Verified Communications and the Phish Bowl, take five minutes to calm down, and don’t act until you are certain.
If you do receive a phish email, report it with the email tools available to you.
Examples of real social engineering attacks at Cornell
These two examples of social engineering attacks that have happened at Cornell and resulted in a stolen NetID. Look for the four tricks described above in each sample email.
Student Financing Opportunity — Apply for Consideration
Dear Student,
The Trump administration in conjunction with Cornell University (2) are disbursing loan to students and staffs in need of financial assistant and I am pleased to inform you that you're eligible (3) to apply for a financing opportunity designed to help qualified students with eligible educational and personal financial needs.
Applicants may be considered for funding between $15,000 and $20,000, depending on eligibility, available funding, verification, and applicable approval requirements. (3)
Potential benefits include:
• Flexible funding options
• Convenient application process
• Funding amounts based on individual eligibility
• Support throughout the application and review process
Ready to apply? Click the application link below to submit your information and request consideration for available funding. (4)
After your application is submitted, eligible applicants may be contacted to complete the verification process. A Zoom meeting may be required to verify your identity, review your application, and discuss the available financing options.
Please note that submitting an application does guarantee approval. All applications are subject to applicable eligibility, verification, underwriting, and approval requirements.
This phish establishes a sense of security with the last two paragraphs, as well as primes the recipient to expect to share personal information with the application “reviewer.” This is sometimes the first step of a multi-step scheme.
Faculty Compliance Notice – Classroom Misconduct Report
Dear Professor,
An anonymous concern was recently submitted regarding conduct observed during one of your lectures. (1) While no formal action is being taken at this time, you are required to review the submitted report and acknowledge the Faculty Code of Conduct response guidelines. (2, 3)
🔒 Review Anonymous Report [Link to Access Concern Portal] (4)
Please note that this is a confidential document and must not be printed, shared, or forwarded. You are not the subject of the concern but may be referenced in a contextual capacity. (3)
Acknowledging this report is necessary to preserve your eligibility for continued in-classroom instruction. (3, 4)
Sincerely,
Comments?
To share feedback about this page or request support, log in with your NetID